DNS Propagation Explained for Faster Launches
DNS propagation explained: learn why domain updates take time, how TTL and caching affect changes, and how to launch your site with fewer launch delays.
ACMMAX Insights ·
A new website can be fully deployed, your domain can be connected, and your browser can still show an old page or an error. That gap is where DNS propagation explained becomes useful. The issue is rarely that your website is broken. More often, different networks are still using cached DNS information from before you made the change.
For entrepreneurs, agencies, and operators working on launch deadlines, this distinction matters. DNS changes do not update every device, browser, internet provider, and resolver at the same second. Knowing what is happening behind the scenes helps you avoid unnecessary rebuilds, support tickets, and last-minute panic.
DNS Propagation Explained: What Actually Happens
DNS, or the Domain Name System, converts a domain name such as yourbusiness.com into the IP address or service endpoint needed to reach your website, email provider, application, or storage service. It is often compared to a phone book, but for online operations it is better understood as the routing layer for your digital assets.
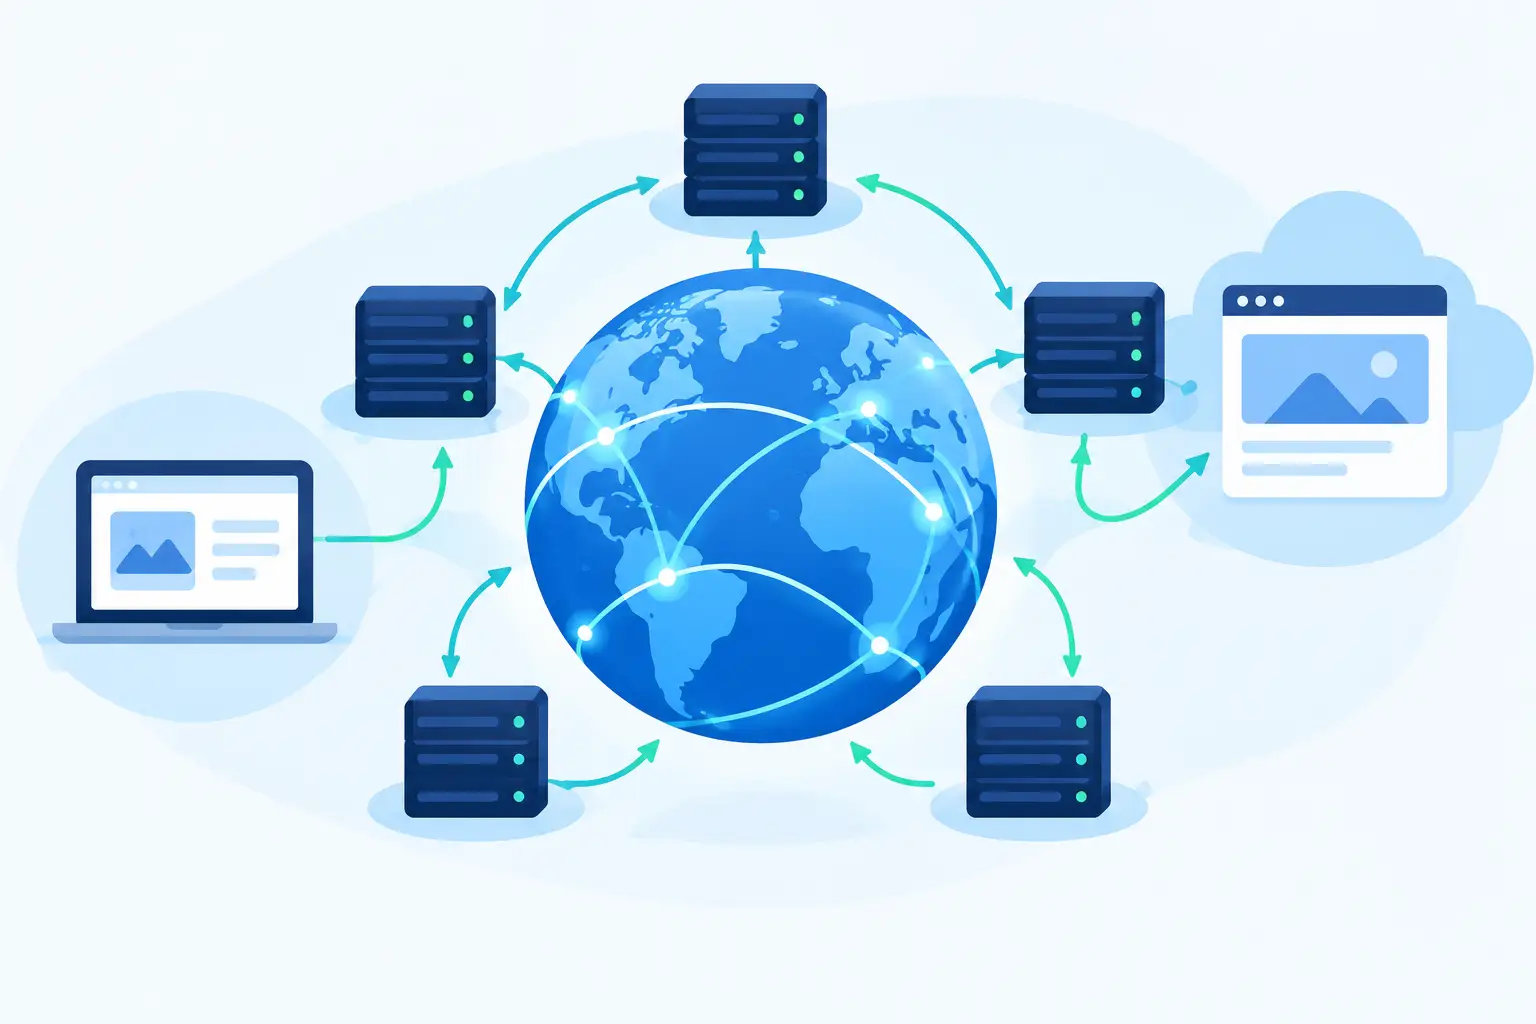
When someone enters your domain in a browser, their device asks a DNS resolver for the answer. The resolver may already have that answer stored in its cache. If it does, it returns the cached result until the record's TTL, or Time To Live, expires. If it does not, it follows the DNS chain to find the authoritative nameserver for your domain and retrieves the current record.
This is why "propagation" is not a single update being pushed across the internet. Your authoritative DNS provider updates the record quickly, often within seconds or minutes. The delay comes from caches across the internet continuing to honor the previous answer for a defined period.
A visitor in Texas, a client using a corporate network in London, and your own laptop may receive different answers temporarily. They may use different DNS resolvers, each with its own cache state. That can make a completed DNS update look inconsistent when it is functioning exactly as designed.
The DNS records that commonly cause launch delays
The record type you change determines what visitors or services experience. An A record points a domain or subdomain to an IPv4 address. An AAAA record does the same for IPv6. A CNAME record aliases one hostname to another, which is common when connecting hosted platforms and verification services.
MX records control where business email is delivered. TXT records are used for domain verification, SPF, DKIM, and DMARC email authentication. Nameserver changes tell the internet which DNS provider is authoritative for the entire domain, so they can have a wider operational effect than editing a single A record.
Changing an A record may move a website to a new server. Updating MX or TXT records may affect email delivery and sender verification. Switching nameservers can expose a missing record set if the new DNS zone was not copied correctly. The technical process is similar, but the business risk is not.
Why DNS Changes Take Time
TTL is the main factor. Every DNS record has a TTL value, expressed in seconds. A TTL of 3,600 means resolvers can cache the answer for up to one hour before requesting a fresh result. A TTL of 86,400 can keep an old answer in circulation for up to 24 hours.
Lower TTL values give you more flexibility before a planned migration because caches refresh more often. The trade-off is that DNS resolvers make more frequent requests to your authoritative nameservers. For most small business sites, a lower TTL during a move is practical. After the move is stable, a moderate TTL can reduce needless lookups without making future changes painfully slow.
There are other variables as well. Browsers may cache DNS. Operating systems can cache it. Office routers, internet service providers, VPNs, and security tools may use their own resolver behavior. Some DNS providers also apply a short negative cache when a record or hostname did not exist at the time of a lookup.
The phrase "DNS propagation takes 24 to 48 hours" is a useful worst-case expectation, not a rule. Many A, CNAME, and TXT record changes become visible in minutes when TTL values are low and caches refresh quickly. Nameserver changes and records with longer existing TTLs often deserve more time. The right expectation depends on what was changed, the prior TTL, and where your users are resolving DNS.
A Practical Timeline for Domain Changes
If you are moving a site or connecting a domain to a new service, plan the DNS work before your public deadline. The current TTL matters more than the TTL you set after the change. If a record currently has a 24-hour TTL, reducing it to five minutes right before a migration does not clear caches that already stored the old record for 24 hours.
A safer workflow is to lower the TTL 24 to 48 hours before a planned switch, then make the record change after the previous cache window has passed. Keep the old hosting environment live during that transition. Once traffic is consistently reaching the new destination, restore a sensible TTL.
For a first-time site launch, the risk is lower because there is no active site to preserve. Even then, check that the domain resolves correctly before announcing it. If business email is involved, treat email DNS records separately. A website can be reachable while email is still misconfigured, and the reverse is also true.
What to check before you change DNS
Use this short operational checklist when a domain points to a new website, cloud VM, managed hosting account, or email platform:
- Confirm which DNS provider is authoritative for the domain. Editing records in a dashboard that is not authoritative will not change public DNS.
- Record the current A, AAAA, CNAME, MX, and TXT entries before making changes. This gives you a fast rollback path.
- Check for an AAAA record when changing an A record. If an outdated IPv6 record remains, some visitors may still reach the wrong destination.
- Reduce TTL before a scheduled migration, not at the moment you need the change to appear.
- Keep the prior website or server available until the new destination has been tested from multiple networks.
How to Tell Whether DNS Is Still Propagating
Start by checking the authoritative record, not only what appears in your browser. If the authoritative nameserver returns the new value, your DNS provider has accepted the update. If public resolvers return different values, you are likely seeing normal cache expiration rather than a failed configuration.
Test from more than one network. Your mobile connection, home Wi-Fi, office network, and a VPN may return different results during the transition. This is useful evidence. If one network reaches the new site and another reaches the old site, propagation is the likely explanation.
Do not judge a DNS change solely by one browser tab. Try a private browsing window to reduce browser cache effects, but remember that private mode does not bypass your network's DNS resolver. Clearing a local DNS cache can help your own device test again, yet it cannot force everyone else's resolver to forget the old record.
If the problem persists beyond the expected TTL, look for configuration issues. Common causes include a typo in the target hostname, an old AAAA record, conflicting CNAME and A records on the same hostname, incorrect nameservers at the registrar, or a missing DNS zone after a nameserver migration. For email, one missing character in an SPF or DKIM record can produce delivery failures even when the domain itself resolves normally.
Avoiding Costly DNS Mistakes
DNS is easy to change and easy to underestimate. Avoid making multiple record edits at once unless they are part of a documented migration plan. When several variables change together - nameservers, hosting, email routing, SSL settings, and redirects - troubleshooting becomes slower because there is no clear source of failure.
Centralized operations make this easier. When your domain, hosting, business email, and deployment tools are managed from fewer places, you spend less time tracking which dashboard controls each layer. ACMMAX is built around that practical advantage: giving growing businesses a single operational center rather than another stack of disconnected vendors.
The best DNS strategy is not to eliminate propagation. Caching exists to keep the internet fast and resilient. The goal is to plan around it: lower TTLs before critical moves, preserve your old environment during the transition, verify records methodically, and give caches time to refresh. That approach turns DNS from a launch-day surprise into a manageable part of running your online business.