How Does DNS Propagation Work After a Domain Change?
Learn how does DNS propagation work, why records update at different speeds, and how to plan domain, hosting, and email changes with less downtime risk.
ACMMAX Insights ·
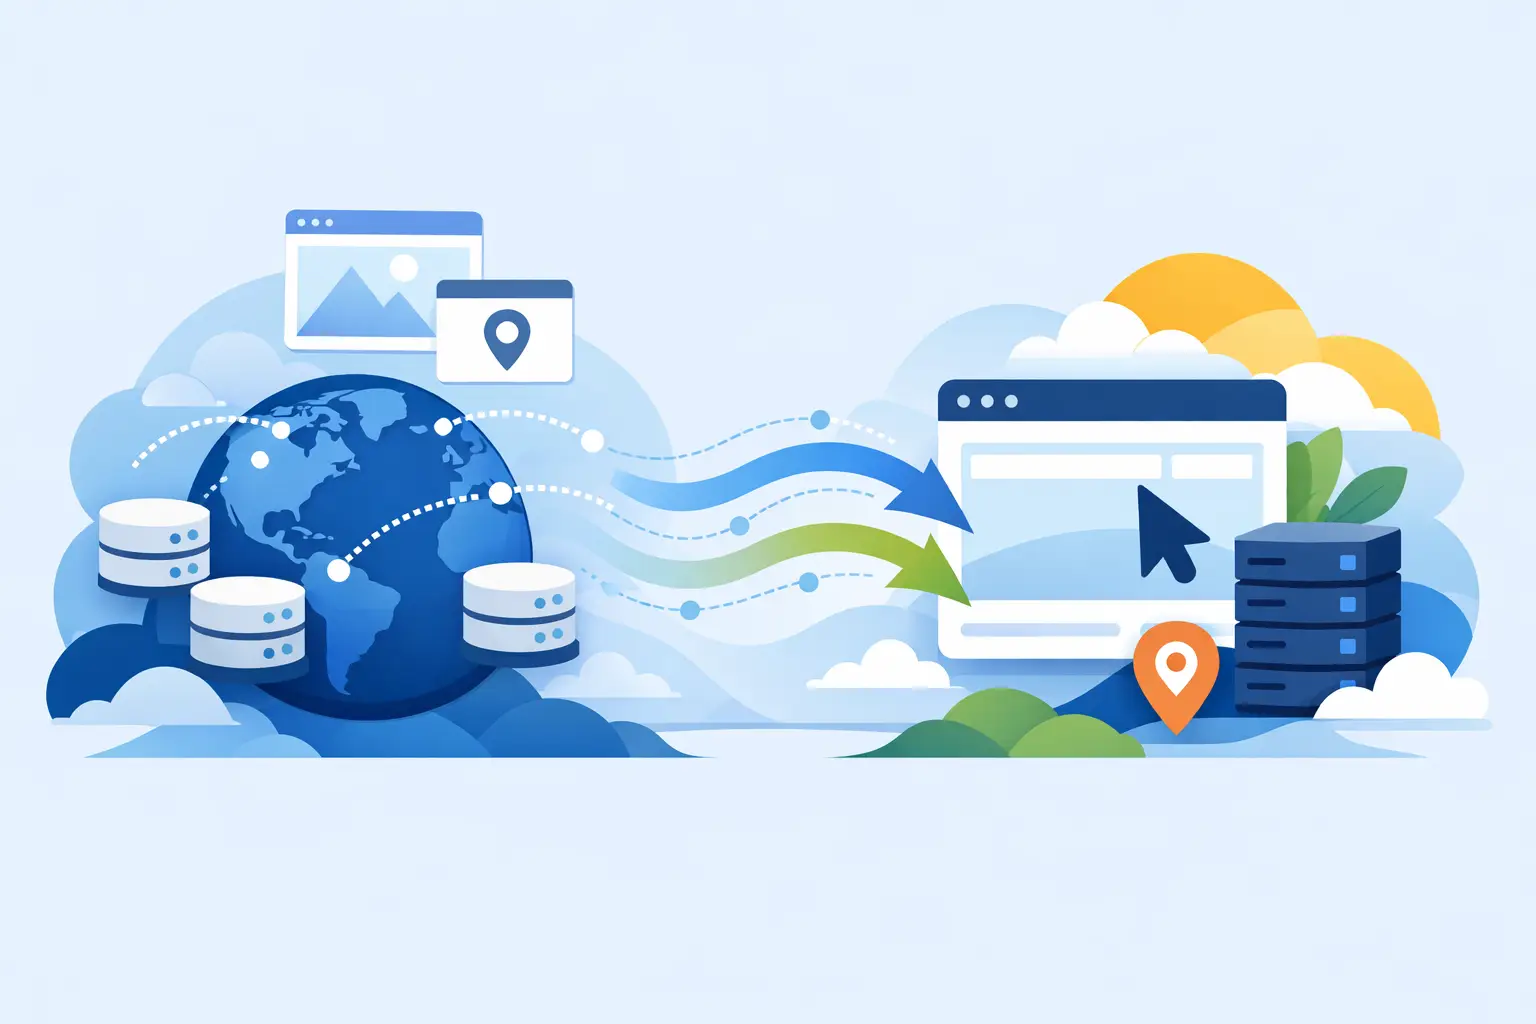
A website can be fully deployed on its new server and still appear unavailable to part of your audience. Your email can be correctly configured but fail for a few users. That gap is usually not a hosting failure. It is DNS propagation. So, how does DNS propagation work when you change where a domain points? It is the process of DNS resolvers worldwide replacing older saved answers with your new DNS records.
For entrepreneurs, agencies, and online operators, the practical issue is simple: DNS changes are not always visible everywhere at the same moment. Knowing what happens behind the scenes helps you plan domain moves, website launches, email setup, and infrastructure changes without unnecessary downtime.
How Does DNS Propagation Work?
DNS, or the Domain Name System, translates human-friendly domain names into the technical destinations that browsers and mail servers need. When someone types yourdomain.com, their device needs an answer to a question such as, "What IP address hosts this website?" DNS provides that answer through records stored in a chain of authoritative systems.
Your domain's DNS zone may contain an A record for a website's IPv4 address, an AAAA record for IPv6, a CNAME record that aliases one hostname to another, MX records for email delivery, and TXT records for verification and email authentication. When you update one of these records, the authoritative nameservers can usually provide the new answer quickly. But authoritative nameservers are only one part of the process.
Most visitors do not query your authoritative nameserver every time they visit your site. Their browser, operating system, office network, internet provider, or public DNS service may have already stored the old answer in a cache. That cached answer remains valid until its time to live, or TTL, expires.
Once the TTL expires, the resolver asks for a fresh answer. It then receives your updated record, stores it according to the new TTL, and sends the visitor to the new destination. Because caches expire at different times, people in different locations can receive different answers during the transition period.
This is why one teammate may see your new site while another still sees the old server. Both results can be technically correct at that moment.
The DNS lookup path in plain English
A typical lookup begins on the visitor's device. If the device has no cached answer, it asks a recursive resolver, often operated by an ISP, workplace, router, or public DNS provider. If that resolver also has no valid cached record, it follows the DNS hierarchy: root servers direct it toward the appropriate top-level domain, the top-level domain directs it to your domain's authoritative nameservers, and those nameservers return the current record.
The resolver caches the result before returning it to the visitor. That cache is useful. Without it, every page load across the internet would create far more DNS traffic and feel slower. The trade-off is that record changes are not instantly reflected in every cache.
What Actually Determines DNS Propagation Time?
You will often hear that DNS propagation takes 24 to 48 hours. That is a safe planning window, not a timer that starts and ends the same way for every change. Many updates become visible in minutes. Others take longer because of record type, TTL settings, cached data, nameserver changes, or local network behavior.
TTL is the main variable you control. A record with a 3,600-second TTL can be cached for up to one hour after a resolver receives it. A record with an 86,400-second TTL can be cached for up to 24 hours. Lower TTLs make changes faster to roll out after caches refresh, but they also cause more frequent DNS lookups. For most small business websites, that extra lookup load is rarely a major concern. For high-volume services, it can be worth balancing flexibility against DNS query volume.
The key detail is timing. Lowering a TTL immediately before a migration does not erase caches that already stored the old, higher TTL. If you plan to move a website or mail service, reduce relevant TTLs at least one full old TTL period before the change. Then wait for existing cached responses to age out.
Changing a record inside the same DNS zone is usually the most predictable scenario. Changing nameservers can involve additional delegation updates at the registrar and cached referrals higher in the DNS chain. It can still complete quickly, but it deserves a wider maintenance window and more careful validation.
DNS Records That Matter During a Move
Not every DNS record affects the same part of your business. A website migration often changes an A record, AAAA record, or CNAME. An email migration affects MX records and commonly TXT records for SPF, DKIM, and DMARC. A missed record can create a confusing partial outage where the website works but email fails, or the main domain works while www does not.
Before making changes, inventory the active records in your DNS zone. Focus on records that power live services, including web traffic, business email, subdomains, verification records, third-party tools, and API endpoints. Keep a copy of the existing zone so you can restore a known-good configuration if needed.
Be especially careful with CNAME records. A hostname with a CNAME generally should not also have other conflicting record types. The root domain, sometimes called the apex, has its own limitations depending on the DNS provider. If you need a root domain to point to a hosted platform, verify whether the provider supports A records, ALIAS or ANAME-style records, or another documented approach.
A Practical DNS Change Plan
The fastest way to prevent avoidable disruption is to prepare before the update rather than troubleshoot after customers report a problem. For a planned website, hosting, or email move, use this sequence:
- Document the current DNS zone. Record each live hostname, its record type, target, TTL, and purpose. Do not assume that a record is unused because its name is unfamiliar.
- Lower TTLs in advance. If the current TTL is 24 hours, lower it at least 24 hours before the planned change. A 300- to 3,600-second TTL is often practical during a controlled migration.
- Build and test the destination first. Confirm that the new server, managed hosting environment, or mail service works before DNS sends public traffic there. Test with temporary host mappings or the provider's preview method when available.
- Update only the records required for the change. Avoid cleaning up unrelated records during a production cutover. Fewer moving parts means fewer opportunities for mistakes.
- Verify from multiple networks. Check the domain using mobile data, home internet, and a separate DNS resolver if possible. This helps distinguish true DNS issues from a cached result on your local network.
- Keep the old service active during the transition. Leave the previous website or mail environment available until propagation has stabilized and critical traffic is reaching the new destination.
For business email, run extra checks. Confirm inbound delivery, outbound sending, SPF alignment, DKIM signing, and DMARC behavior. Email is less forgiving than a web page because a failed message may not be retried forever, and customers may not tell you it bounced.
Common DNS Propagation Myths
The first myth is that DNS propagation means records are physically copied across every server on the internet. In most cases, no central copying event occurs. Resolvers simply discard old cached answers when they expire and retrieve the current answer from the authoritative source.
The second myth is that clearing your browser cache fixes propagation. It may fix a browser-level issue, but DNS can also be cached by your operating system, router, corporate network, or resolver. A private browsing window may not change the result if the answer is cached upstream.
The third myth is that any delay means something is broken. A short period of mixed results is expected after a legitimate DNS change. The warning signs are different: missing records, incorrect nameservers, expired domain registration, inconsistent targets, or a new server that is not ready to accept traffic.
When Propagation Is Not the Real Problem
If your domain has been pointing to a new destination longer than the relevant TTL window and the result is still inconsistent, investigate configuration rather than waiting indefinitely. Check that the domain is using the nameservers you expect, the records were saved in the active DNS zone, and there are no duplicate or conflicting entries.
Also check the destination itself. A web server may need the domain added as a site or virtual host. SSL certificates may need time to issue after DNS validates ownership. A firewall may block web traffic even when DNS resolves perfectly. For email, the receiving provider may reject messages because the MX hostname, SPF record, or DKIM key is wrong.
Centralized domain, hosting, and email management reduces the chance of these handoff errors. When your core services are visible in one operating environment, it is easier to confirm which record points where, which server is active, and whether the destination is actually ready. That is the operational advantage platforms such as ACMMAX are designed to provide for businesses that need to launch and move quickly.
DNS propagation is not a mystery or a waiting game you cannot control. Set realistic TTLs, prepare the destination before switching traffic, preserve the old service during the overlap, and validate the records that keep your website and email running. Those few decisions turn a potentially disruptive domain change into a controlled release.